
Last updated on September 30, 2026
Overview of MFA for SSH on Linux
Rublon MFA for Linux SSH uses Pluggable Authentication Modules (PAM) to add multi-factor authentication to Linux services. In addition to SSH logins, the connector can protect privilege elevation through sudo and su, graphical desktop logins, and other applications that support PAM authentication. Each service requires an appropriate PAM configuration. Interactive MFA is available only in SSH sessions that support the required user interaction. Desktop logins and other PAM services require non-interactive mode (nonInteractiveMode=true), which does not display an authentication method selection menu or ask the user to enter a passcode.
Supported Systems
- Debian (11, 12)
- Ubuntu (18.04, 20.04, 22.04, 24.04)
- Red Hat / CentOS / Alma / Rocky (8, 9) / Oracle Linux (8, 9)
- openSUSE Leap / SUSE Linux Enterprise Server 15 SP3*
- Oracle Solaris 11.4 (x86)
* Rublon for SSH is not compatible with SUSE Linux Enterprise Server 11 and 12 due to their outdated versions of GCC. If this is a requirement for you, contact Rublon Support.
Minimum Hardware Requirements:
- 1 CPU core
- 10 MB free disk space
- 10 MB RAM
Note: The connector itself uses only a small amount of CPU and typically consumes tens of kilobytes of memory during operation. The figures above include additional runtime overhead required by the application, shared libraries, and system environment.
Supported Authentication Methods
| Authentication Method | Supported | Comments |
| Mobile Push | ✔ | N/A |
| FIDO | – | N/A |
| Passcode | ✔ | N/A |
| SMS Passcode | ✔ | N/A |
| SMS Link | ✔ | N/A |
| Phone Call | ✔ | N/A |
| QR Code | – | N/A |
| Email Link | ✔ | N/A |
| YubiKey OTP | ✔ | N/A |
| RFID | – | N/A |
Demo Video

Network Diagram

- Initiate the SSH connection.
- Perform the first factor of authentication using your primary authentication source.
- The Rublon for Linux SSH connector establishes a connection to the Rublon API over TCP port 443.
- Perform the second factor of authentication using Rublon MFA.
- The Rublon for Linux SSH connector receives the authentication result.
- Access to the SSH session is granted.
Known Limitations
- If a user has enrolled multiple Phones, only the MFA methods available for the Phone that was selected as default are displayed in the SSH connector. There is no option to switch to another Phone.
- After enrolling a Phone Number for SMS authentication or enrolling the Rublon Authenticator app, the system prioritizes one of these authenticators over the other. In certain circumstances, the authentication methods associated with the former authenticator may become unavailable in the SSH interface.
Before You Start
Create an Application in the Rublon Admin Console
1. Sign up for the Rublon Admin Console. Here’s how.
2. In the Rublon Admin Console, go to the Applications tab and click Add Application.
3. Enter a name for your application (e.g., Linux SSH) and then set the type to Linux SSH.
4. Click Save to add the new application in the Rublon Admin Console.
5. Copy and save the values of the System Token and Secret Key. You are going to need these values later.
Install Rublon Authenticator
Some end-users will install the Rublon Authenticator mobile app. So, as a person configuring MFA for Linux SSH, we highly recommend you install the Rublon Authenticator mobile app, too. Thanks to that, you will be able to test MFA for Linux SSH via Mobile Push.
Download the Rublon Authenticator for:
Installing Rublon MFA for Linux SSH
1. Download the package for your Linux distribution.
2. Install the package.
Ubuntu & Debian:
For Ubuntu (20.04, 22.04, 24.04) and Debian (11, 12), use:
sudo dpkg -i <package_name>RHEL, AlmaLinux, Rocky Linux, Oracle Linux & CentOS:
Use the following installation command:
sudo yum install <package_name>openSUSE Leap / SUSE Linux Enterprise Server 15 SP3:
sudo zypper install <package_name>Note
You can use the rpm -i <package_name> command instead, but keep in mind that this command performs a check to determine if the policycoreutils-python-utils package is already installed. If the package is not installed, the installation of the module will not end successfully and you will have to install it manually using the sudo yum install -y policycoreutils-python-utils command before trying rpm -i again.
In contrast, if you use yum install, a check will be performed and in case the policycoreutils-python-utils package is not found, it will be automatically installed along with Rublon for Linux. For that reason, we recommend you use the yum install command to install Rublon MFA for Linux on RHEL and CentOS distributions.
3. Edit the rublon.config file using the nano /etc/rublon.config command and then:
- Paste the values of the System Token and Secret Key from the application with the type Linux SSH added in the Applications tab of the Rublon Admin Console that you have copied before.
- Adjust other options according to your preferences or leave the default values. Refer to Updating the Configuration File for more information about each option.
4. Manually adjust the SUDO service configuration and SU service configuration.
5. Optionally enable Rublon MFA for SSH Key Authentication or enable Rublon MFA for Active Directory.
6. Optionally, configure Append Mode or Offline Mode.
Updating the Configuration File
The Rublon for Linux SSH connector uses the rublon.config configuration file, which contains the necessary and optional options for Rublon MFA for Linux SSH authentication.
The configuration file is located in the following location:
/etc/rublon.config| Option | Description |
| systemToken | The System Token of the application with the type Linux SSH added in the Applications tab of the Rublon Admin Console |
| secretKey | The Secret Key of the application with the type Linux SSH added in the Applications tab of the Rublon Admin Console |
| rublonApiServer | The URL of the Rublon API. Default: https://core.rublon.net |
| failMode | Either “bypass” or “deny”. This option allows you to set what should happen in case of configuration errors or when the Rublon API is unreachable. Default: “bypass” |
| prompt | This option allows you to define the maximum number of authentication prompts displayed before access is denied. You can set this value to 1, 2, or 3. For the Default Authentication Method, such as Auto Push, it is recommended to set this option to 1 for optimal security. Default: 1 |
| logging | When set to “true”, this option allows the saving of event logs from the pam_rublon module to a file located under /var/log/rublon-ssh.log. Default: “true” |
| autopushPrompt | If the Default Authentication Method is set to Mobile Push and the autopushPrompt option is set to true, then every time your users choose the Mobile Push authentication method when logging in, they will be informed a push notification has been sent to their phone. Default: “false” |
| nonInteractiveMode | When set to “true”, the connector operates in a completely non-interactive mode. Instead of prompting the user to select an authentication method, it automatically chooses the first supported method by sequentially attempting methods in the following order: Push, Email, SMS Link, and Phone Call. Offline Mode is unavailable when this option is set to “true”, including when it is enabled through a per-service PAM override. Default: “false” |
| appendModeDelimiter | Separator between the password and the appended MFA method or code. Used only by pam_rublon_append.so. You can override this setting by passing an argument to that module in the PAM service configuration. Setting this option alone does not enable Append Mode. For more information, see Append Mode. Default: , (comma) |
| offlineBypass | Enables Offline Mode, which verifies Mobile Passcodes locally when the Rublon API cannot be reached. Requires interactive mode and a previously stored offline secret for the user. Despite its name, this option enables offline MFA verification rather than skipping MFA. Accepted values: 1, true, yes, on to enable; 0, false, no, off to disable. Values are case-insensitive. Disabled by default. For more information, see Offline Mode. |
| rpskDir | Directory containing per-user secrets used for offline authentication. The connector creates the directory when first saving a secret, provided that its parent directory already exists. If you use a custom path, create the directory before using Offline Mode and set its owner and group to root:root with permissions 0700. Offline secret files (.rpsk) must be owned by root:root with permissions 0600, allowing only root to read and write them. Default on Linux: /var/lib/rublon. For more information, see Offline Mode. |
| proxyEnabled | When set to “true”, enables proxy. When enabled, one of the following conditions must be met: 1. proxyType and proxyHost (plus optional proxyPort) are provided, or 2. Standard environment variables (e.g., HTTP_PROXY) are already set on the host OS. If both are present, the explicit settings in this file override the environment variables. Default: “false” |
| proxyType | The protocol or scheme that the proxy speaks. Supported values: HTTP – plain HTTP tunnel Required if proxyEnabled is set to “true” and the client is not relying on environment variables. |
| proxyHost | Hostname or IP address of the proxy server. Required when proxyEnabled is set to “true” and the client is not relying on environment variables. |
| proxyPort | TCP port on which the proxy listens. If omitted, the connector falls back to common defaults (HTTP = 8080). |
| proxyAuthRequired | When set to “true”, the proxy expects credentialed (Basic) authentication. If enabled, both proxyUsername and proxyPassword must be provided. Default: “false” |
| proxyUsername | Username used for proxy authentication. Required only when proxyAuthRequired is set to “true”. |
| proxyPassword | The password of the proxy server user. Required only when proxyAuthRequired is set to “true”. |
Per-Service Overrides
Since version 2.3.2, the connector can read module arguments (Rublon options) defined directly in PAM service files (for example, /etc/pam.d/sshd, /etc/pam.d/sudo, /etc/pam.d/su).
When present, arguments defined in these files override the corresponding settings from /etc/rublon.config for that specific PAM service only.
This overriding ability lets you keep a global baseline in /etc/rublon.config and apply stricter or different behavior per service (e.g., stronger security on sshd, different UX for sudo).
Example – force non-interactive mode only for SSH:
In /etc/pam.d/sshd, append the Rublon options you want for SSH after the mention of the pam_rublon.so module:
auth sufficient pam_rublon.so nonInteractiveMode=trueSSH logins will use nonInteractiveMode=true, while other services (e.g., sudo, su) will continue to use the value from /etc/rublon.config unless you also override them in their own PAM files. This follows standard Linux-PAM semantics: each file under /etc/pam.d/ is a per-service policy where you can pass module-specific arguments.
Append Mode
Append Mode allows users to enter their password and an MFA method name or code in the same password prompt. For example, with a comma as the separator, entering MyPassword,123456 supplies the password and a Passcode together.
For supported values and login examples, see the Append Mode user guide.
Enable Append Mode
Append Mode is not enabled automatically during installation.
1. Open the PAM configuration for the service you want to configure. For SSH, edit:
/etc/pam.d/sshd2. Add the following line as the first entry in the service’s authentication stack:
auth required pam_rublon_append.soThis entry must precede all other auth modules and any entries that include authentication rules, such as @include common-auth or auth substack password-auth.
The pam_rublon_append.so module separates the password from the appended value. It does not verify the password. Keep the existing pam_rublon.so entry in place after primary authentication.
3. Optionally, set the separator in /etc/rublon.config:
appendModeDelimiter=,If this setting is absent, the connector uses a comma. You can also set the separator for an individual service by passing it directly to the Append Mode module:
auth required pam_rublon_append.so appendModeDelimiter=,The module argument takes precedence over /etc/rublon.config. Pass this argument to pam_rublon_append.so. Note that pam_rublon.so does not use it.
4. Keep a root shell session open and test authentication in a separate session before closing it.
The same module ordering requirement applies when configuring Append Mode for other PAM services, including sudo, su, and graphical logins.
Behavior and Limitations
- Method names are case-sensitive. Append Mode can select only methods available to the user.
- The keyword sms is not supported. A six-digit appended code is treated as a Mobile Passcode, not an SMS Passcode.
- The combined password, separator, and appended value must not exceed 256 bytes. The appended value must not exceed 44 characters.
- The input is split at the last occurrence of the separator. Choose a separator that does not occur in users’ passwords to avoid incorrect password parsing when a user enters a password without an appended value.
- The separator cannot be
#,[,],=, whitespace, or a NUL character. An invalid separator setting produces a warning in the connector log and falls back to a comma. - If no separator is present, authentication follows the normal flow. In interactive SSH sessions, an unrecognized appended value or an unavailable method returns the user to the normal interactive method selection.
- An appended code is submitted only once. In interactive SSH sessions, any subsequent attempts after a rejected code use interactive prompts.
Offline Mode
Offline Mode allows users to complete MFA with a Mobile Passcode when the connector cannot reach the Rublon API. The passcode is verified locally using an offline secret previously saved on the machine for that user.
Offline Mode requires an SSH session that supports interactive passcode entry and nonInteractiveMode=false. It is not available for desktop logins or other PAM services that require non-interactive mode.
The system must still verify the user’s password or other configured primary credentials. Offline Mode handles the second authentication step by checking the user’s Mobile Passcode locally when the Rublon API cannot be reached.
Enable Offline Mode
Offline Mode is disabled by default.
1. Add the following setting to /etc/rublon.config:
offlineBypass=true2. Ensure that interactive mode is enabled:
nonInteractiveMode=falseCheck the PAM service configuration for overrides. A service configured with nonInteractiveMode=true cannot use Offline Mode.
3. While the Rublon API is reachable, have each user complete a successful online MFA login on the machine. The connector retrieves and saves the user’s offline secret during successful online authentication.
4. Verify that the user’s secret file has been saved before relying on Offline Mode. On Linux, the default location is /var/lib/rublon/USERNAME.rpsk, where USERNAME is the username used by the connector.
A user without a saved secret cannot complete offline MFA. A successful online login alone does not guarantee that the secret was saved if the storage directory is inaccessible or unwritable.
Authentication Behavior
If the Rublon API cannot be reached and the Offline Mode requirements are met, the connector asks the user for a Mobile Passcode from their authenticator app. It checks the code locally using the user’s stored offline secret, allowing the user to complete MFA without a connection to the Rublon API.
If the user already entered a Mobile Passcode before the connection failed, the connector checks that code locally without asking the user to enter it again.
An incorrect offline passcode is rejected.
Offline Mode is triggered by connection failures, such as connection timeouts or TLS connection errors. It is not triggered when the Rublon API responds with a rejection, such as an invalid request signature or an expired transaction.
When Offline Mode is enabled and all its requirements are met, a connection error triggers local Mobile Passcode verification regardless of whether failMode is set to bypass or deny. If the user’s saved offline secret is missing or cannot be read, the connector follows the failMode setting.
Requirements and Limitations
- Only Mobile Passcode authentication is supported offline. Other authentication methods are unavailable.
- Before using Offline Mode, the user must complete a successful online MFA login on the same machine, and the connector must successfully save the user’s offline secret.
- Only one offline secret is stored per user.
- Offline Mode requires interactive authentication and is unavailable with nonInteractiveMode=true.
- The username must not contain a forward slash (
/) and must be no longer than 64 bytes. Periods (.) within the username are allowed. - Keep the machine’s clock synchronized with the authenticator device. Offline verification accepts the current 30-second TOTP time step without a tolerance window for adjacent steps.
Offline Secret Storage
On Linux, offline secrets are stored in /var/lib/rublon by default. You can change this location with rpskDir.
Secret files contain sensitive authentication material and are not encrypted at rest. Restrict access to the directory and its contents. The directory should be owned by root with permissions 0700, and secret files should be owned by root with permissions 0600.
The connector creates the directory when it first saves a secret, but it does not create missing parent directories or correct permissions on an existing directory. Prepare a custom directory before configuring it.
Changing rpskDir does not automatically move existing secrets. Verify that each user has an available secret in the configured location before relying on offline authentication.
Modifying the SUDO Service Configuration
To use the Rublon PAM module, various configuration files related to the sudo service have to be modified.
We recommend you leave at least one root shell session active and open while making any changes to your PAM configuration to prevent accidentally locking yourself out.
Debian and Ubuntu
Edit the /etc/pam.d/sudo file. Change entry:
@include common-authTo:
#@include common-auth
auth required pam_env.so
auth requisite pam_unix.so
auth sufficient pam_rublon.so nonInteractiveMode=true
auth required pam_deny.so
Note: Starting from version 2.3.2 of the connector, arguments supplied to pam_rublon.so in this file take precedence over the same options in /etc/rublon.config for this service only. Simply append the arguments to be overridden after line auth sufficient pam_rublon.so. More information: Per-Service Overrides.
To use Append Mode with this service, add auth required pam_rublon_append.so as the first entry in its authentication stack. Keep the existing password verification and pam_rublon.so entries. See Append Mode.
CentOS and RHEL
Edit the /etc/pam.d/sudo file. Change entry:
auth include system-authTo:
#auth include system-auth
auth required pam_env.so
auth requisite pam_unix.so
auth sufficient pam_rublon.so nonInteractiveMode=true
auth required pam_deny.so
Note: Starting from version 2.3.2 of the connector, arguments supplied to pam_rublon.so in this file take precedence over the same options in /etc/rublon.config for this service only. Simply append the arguments to be overridden after line auth sufficient pam_rublon.so. More information: Per-Service Overrides.
To use Append Mode with this service, add auth required pam_rublon_append.so as the first entry in its authentication stack. Keep the existing password verification and pam_rublon.so entries. See Append Mode.
Modifying the SU Service Configuration
To use the Rublon PAM module, various configuration files related to the su service have to be modified.
We recommend you leave at least one root shell session active and open while making any changes to your PAM configuration to prevent accidentally locking yourself out.
Debian and Ubuntu
Edit the /etc/pam.d/su file. Change entry:
@include common-authTo:
#@include common-auth
auth required pam_env.so
auth requisite pam_unix.so
auth sufficient pam_rublon.so nonInteractiveMode=true
auth required pam_deny.so
Note: Starting from version 2.3.2 of the connector, arguments supplied to pam_rublon.so in this file take precedence over the same options in /etc/rublon.config for this service only. Simply append the arguments to be overridden after line auth sufficient pam_rublon.so. More information: Per-Service Overrides.
To use Append Mode with this service, add auth required pam_rublon_append.so as the first entry in its authentication stack. Keep the existing password verification and pam_rublon.so entries. See Append Mode.
CentOS and RHEL
Edit the /etc/pam.d/su file. Change entry:
auth substack system-authTo:
#auth substack system-auth
auth required pam_env.so
auth requisite pam_unix.so
auth sufficient pam_rublon.so nonInteractiveMode=true
auth required pam_deny.so
Note: Starting from version 2.3.2 of the connector, arguments supplied to pam_rublon.so in this file take precedence over the same options in /etc/rublon.config for this service only. Simply append the arguments to be overridden after line auth sufficient pam_rublon.so. More information: Per-Service Overrides.
To use Append Mode with this service, add auth required pam_rublon_append.so as the first entry in its authentication stack. Keep the existing password verification and pam_rublon.so entries. See Append Mode.
Enable Rublon MFA for SSH Key Authentication (Optional)
Enabling SSH key authentication enhances the security of your system by enforcing key-based authentication with Rublon MFA, and disabling the less secure password-based login.
If you do not use SSH key authentication (i.e. skip this section altogether), the Rublon MFA for Linux SSH connector works in the following way:
- Logging in with a key does not challenge for Rublon MFA.
- Logging in with a password does challenge for Rublon MFA.
If you use SSH key authentication (i.e. complete all steps from this section), the Rublon MFA for Linux SSH connector works in the following way:
- Logging in with a key does challenge for Rublon MFA.
- Logging in with a password is not possible.
We recommend you leave at least one root shell session active and open while making changes to your PAM configuration to prevent accidentally locking yourself out. Additionally, always make sure your PAM configuration works locally before testing it with SSH logins.
To enable MFA when using SSH key-based authentication, you need to configure PAM accordingly. Run one of the following scripts (as root or with sudo), depending on your Linux distribution:
Ubuntu/Debian:
sudo sh /usr/share/rublon/inst_pubkey.shRHEL, AlmaLinux, Rocky Linux, Oracle Linux 8 & CentOS 8:
sudo sh /usr/share/rublon/inst_pubkey_rhel_8.shRHEL, AlmaLinux, Rocky Linux, Oracle Linux 9 & CentOS 9:
sudo sh /usr/share/rublon/inst_pubkey_rhel_9.shThese scripts will update your system’s PAM configuration to ensure that Rublon MFA is applied during SSH key authentication.
If you are experiencing issues with your key authentication, refer to SSH Key Authentication Troubleshooting.
Enable Rublon MFA for Active Directory (Optional)
Rublon MFA for Linux SSH is compatible with systems that authenticate users through Active Directory. This includes systems that use modules such as:
- SSSD (pam_sss.so)
- Winbind (pam_winbind.so)
- Other LDAP or identity provider modules
Rublon MFA does not modify or configure your AD integration. The process of joining the Linux host to the domain and enabling AD authentication is entirely managed by your environment and tools (e.g., realm join, SSSD configuration, or Winbind/Samba configuration)
PAM evaluates authentication modules in the order in which they appear. To ensure the standard MFA behavior, where the password challenge comes first, the module responsible for AD authentication must be placed before “auth sufficient pam_rublon.so” in the PAM auth stack.
This means:
- If your system uses SSSD, ensure that pam_sss.so appears before auth sufficient pam_rublon.so.
- If your system uses Winbind, ensure that pam_winbind.so appears before auth sufficient pam_rublon.so.
- Ensure that the PAM control flags do not allow successful primary authentication to skip pam_rublon.so.
This ensures that:
- The system verifies the user’s identity (via AD) first.
- Rublon MFA is triggered only after successful primary authentication.
- No additional changes to your AD, SSSD, Winbind, or LDAP configuration are required.
With Append Mode enabled, pam_rublon_append.so must run before the primary authentication module, including pam_sss.so or pam_winbind.so, and before any entry that includes these modules. The existing pam_rublon.so entry remains after primary authentication.
We recommend you leave at least one root shell session active and open while making changes to your PAM configuration to prevent accidentally locking yourself out. Additionally, always make sure your PAM configuration works locally before testing it with SSH logins.
Enable MFA for PAM on Linux Desktop Logins (Optional)
When Rublon MFA for Linux SSH is enabled in the system’s PAM configuration, the MFA check will also apply to local Linux GUI logins, for example through display managers such as GDM, SDDM, or LightDM.
This behavior results from how PAM processes authentication and should be treated as PAM-based MFA for desktop logins, not as a dedicated graphical MFA feature.
Behavior
During a GUI login, PAM triggers the MFA flow after the user enters their password. The display manager does not show an MFA prompt, method selection screen, or status message. Instead, PAM waits for the MFA result in the background.
For example, if the user approves a Mobile Push notification on their mobile device, the GUI session starts. If the MFA request is rejected, expires, or times out, the login fails, and the user is returned to the login screen.
How to Enable
We recommend you leave at least one root shell session active and open while making changes to your PAM configuration to prevent accidentally locking yourself out.
1. Open the common PAM authentication file:
sudo nano /etc/pam.d/common-auth2. Add the Rublon MFA for Linux module after the rules that validate the primary credentials. Check the PAM control flags to ensure that successful primary authentication reaches pam_rublon.so and cannot skip it. The example below shows a simple Debian/Ubuntu configuration using pam_unix.so.
auth required pam_rublon.so nonInteractiveMode=trueExample:
auth [success=1 default=ignore] pam_unix.so nullok
auth requisite pam_deny.so
auth required pam_permit.so
auth required pam_rublon.so nonInteractiveMode=true
Note: Changes to common-auth affect all services that include this file. Use a service-specific PAM configuration if SSH must retain interactive MFA and Offline Mode.
3. Save the file.
4. Test the configuration by signing in locally with a test user.
Notes
This configuration provides a promptless MFA experience for GUI logins. The user must complete one of the available non-interactive MFA methods, such as Mobile Push, Email Link, SMS Link, or Phone Call.
Because no MFA dialog or status message is shown in the graphical login screen, users should be informed by the organization that they need to complete the MFA request on their mobile device or through another non-interactive method after entering their password.
Append Mode can also be configured for graphical logins, allowing users to specify an MFA method or code in the password field. See Append Mode. Offline Mode is unavailable with the nonInteractiveMode=true configuration shown above.
Auto Push – Use Case
When the Default Authentication Method policy is set to Mobile Push, Rublon MFA automatically sends a notification to the user’s Rublon Authenticator mobile app. This provides an MFA flow without interactive method selection, for example, when using scp or an SFTP client such as FileZilla.
SCP command example
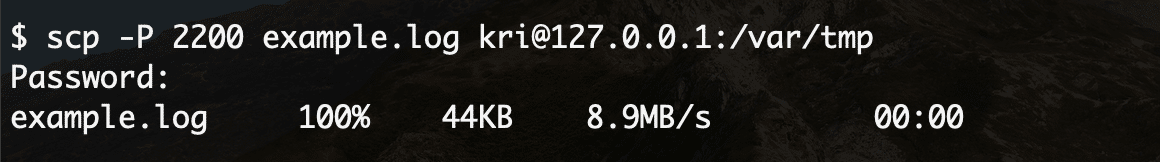
In this scenario, after entering the password, the user accepts the push notification received in the Rublon Authenticator mobile app. The entire process does not display additional messages that appear during standard MFA login via Rublon SSH.
Updating Rublon MFA for Linux SSH
Keep at least one root shell session open throughout the update. Before updating, back up /etc/rublon.config and the PAM and SSH configuration files modified for your integration. If you use Offline Mode, also back up the offline secret directory specified by rpskDir, preserving its ownership and permissions.
1. Download the latest connector package for your Linux distribution.
2. Update the installed package using the appropriate command below. Do not uninstall the existing version first.
Debian and Ubuntu:
sudo dpkg -i <package_name.deb>RHEL, AlmaLinux, Rocky Linux, Oracle Linux, CentOS, and supported SUSE distributions:
sudo rpm -Uvh --nopostun <package_name.rpm>Replace the placeholder with the filename of the downloaded package.
3. After updating, verify that /etc/rublon.config and the PAM configuration for each protected service have been preserved. If you use Append Mode, check the placement of pam_rublon_append.so. If you use Offline Mode, check offlineBypass, any custom rpskDir, and the availability of users’ offline secret files.
4. Test authentication in a separate session before closing the root shell session.
Uninstalling Rublon MFA for Linux SSH
1. Remove the PAM file.
For Debian and Ubuntu, use:
sudo apt purge rublon-ssh-pamFor CentOS, AlmaLinux, Rocky Linux, Oracle Linux, and RHEL, use:
sudo yum remove rublon-sshFor SUSE distributions, use:
sudo zypper remove rublon-sshNote
If the package is not found under this name, use the following command to locate the correct name:
yum list | grep rublon
Then, remove the discovered package with:
yum remove <found-package-name>
2. If Append Mode was configured, also remove or comment out any remaining auth required pam_rublon_append.so entries in the PAM configuration files you modified.
Troubleshooting
Uninstallation and Post-Uninstallation Issues
If you are experiencing issues when trying to uninstall or after uninstalling the connector, remove or comment out the following lines in /etc/pam.d/sshd (the last two lines in the file):
auth required pam_rublon.so
account required pam_rublon.so
Known Issue with Uninstalling version 2.1.X on RHEL 9
When uninstalling Rublon for Linux SSH version 2.1.X on RHEL 9, the process does not remove the Rublon-specific entries from the /etc/pam.d/sshd file. You must manually remove these lines following the guidance in the Uninstallation and Post-Uninstallation Issues section.

SSH Key Authentication Troubleshooting
If you are experiencing issues with Rublon MFA for SSH key authentication, verify all the steps below. These configurations are necessary for proper integration. If any setting is missing or incorrectly configured, Rublon MFA for SSH key authentication may not function as intended.
1. Check the Rublon SSH configuration file:
- RHEL 8: /etc/ssh/01-rublon-ssh.conf
- RHEL 9, Ubuntu, Debian (and others): /etc/ssh/sshd_config.d/01-rublon-ssh.conf
Ensure the file contains the following lines:
UsePAM yes
LoginGraceTime 15m
ChallengeResponseAuthentication yes
AuthenticationMethods publickey,keyboard-interactive
MaxAuthTries 3
PubkeyAuthentication yes
PasswordAuthentication no
2. Check PAM Configuration (/etc/pam.d/sshd):
Debian / Ubuntu:
At the end of the file, ensure these lines are present:
auth  requisite pam_rublon.so
account required pam_rublon.so
Make sure the following line is commented out (prepend # if it’s not already):
#@include common-authRHEL / CentOS:
At the end of the file, ensure this line is present:
auth required pam_rublon.soComment out (prepend #) the following existing entry if present:
#auth substack password-auth3. Verify the SSH Service Status:
RHEL / CentOS:
service sshd statusUbuntu / Debian:
systemctl status sshdAppend Mode Troubleshooting
If Append Mode does not work:
1. Verify that pam_rublon_append.so runs first in the service’s authentication stack, before password verification and included authentication rules.
2. Check the separator in /etc/rublon.config and any appendModeDelimiter argument passed to pam_rublon_append.so.
3. Verify the spelling and capitalization of the appended method name, or check that the code has the required length.
4. Check that the combined input does not exceed 256 bytes and that the appended value does not exceed 44 characters.
5. If the password is rejected before MFA, check whether the separator occurs in the password and causes incorrect parsing.
Offline Mode Troubleshooting
If Offline Mode does not work:
1. Verify that offlineBypass=true is configured and that nonInteractiveMode is not enabled globally or in the PAM service configuration.
2. Check that the user’s .rpsk file exists in the configured rpskDir. Replace USERNAME below with the actual username:
sudo ls -ld /var/lib/rublon
sudo ls -l /var/lib/rublon/USERNAME.rpsk
Use your custom directory if you changed rpskDir. Check ownership, permissions, and any SELinux restrictions that could prevent access.
3. If the file is missing, restore connectivity and complete an online MFA login. Check that the storage directory is writable. Failure to save an offline secret does not prevent an otherwise successful online login.
4. Check that the machine and authenticator device have synchronized clocks.
5. Confirm that the problem is a connection failure. A rejection returned by the Rublon API does not trigger Offline Mode.
When connector logging is enabled, review /var/log/rublon-ssh.log. A missing or unreadable secret file may not produce a specific error message, so also verify the file directly.
Offline secret files contain sensitive authentication material. Do not include their contents in screenshots, support messages, or diagnostic attachments.
General Issues
If you are experiencing issues, make sure the following settings are set in the 01-rublon-ssh.conf file:
ChallengeResponseAuthentication yes
UsePAM yes
PasswordAuthentication yes
On Ubuntu, Debian, and RHEL 9, the 01-rublon-ssh.conf file is located in /etc/ssh/sshd_config.d/. On RHEL 8, the file is located in /etc/ssh/, so make sure that include /etc/ssh/01-rublon-ssh.conf was added to /etc/ssh/sshd_config.
Tip
The sshd -T command is a useful tool when troubleshooting SSH server issues. When you run this command as the root user (you can become root using the sudo command), it will display the current configuration of your SSH server.
This can be very helpful because it allows you to see all the settings that are currently in effect for your SSH server. If there is a problem with your SSH server, this command can help you identify if a particular setting is causing the issue. For example, you might find that a setting is different from what you expected, which could be the cause of the problem.
Also, note that parameters are lowercase. Take it into consideration when using commands with pattern matching like grep.
If you encounter any issues with your Rublon integration, please contact Rublon Support. Make sure to send us a detailed description of the issue you have experienced, along with screenshots and the /var/log/rublon-ssh.log file.
Related Posts
Rublon MFA for SSH (Linux) – Release Notes
Rublon MFA for SSH (Linux) – Download